ITS Security Division

Managed EDR Services for Endpoint Threat Detection and Containment

Detect, investigate, and contain endpoint threats with ITS Managed Endpoint Detection and Response, backed by continuous monitoring and remediation guidance.

Cybersecurity Expertise Backed by Industry Recognition

ITS has earned industry recognition for cybersecurity expertise, managed services, and technology partner performance.
  • CRN MSP 500 2026
  • CRN Tech Elite 250 2026
  • CRN Security 100 2026
  • Cloudtango's MSP Select 2026
  • SonicWall MSP Partner of the Year 2026

What Risks Come from Gaps in Endpoint Protection?

Without continuous monitoring, automated containment, and rapid remediation, endpoint threats can go undetected, spread across your network, and disrupt operations.

Modern Threats Can Bypass Traditional Antivirus

Traditional, signature-based antivirus may fail to detect fileless attacks, emerging exploits, and suspicious behavior that does not match a known malware signature.

Compromised Endpoints Can Spread Threats Across Your Network

Once an attacker gains access to one device, they may attempt to reach other accounts, devices, and systems when isolation controls are not in place.

Security Teams Lack Real-Time Endpoint Visibility

Without continuous endpoint monitoring, suspicious activity may remain undetected while an attacker attempts to access other systems or data.

Manual Endpoint Remediation Can Slow Recovery

Identifying, isolating, and restoring a compromised endpoint manually can extend recovery times, increase incident costs, and prolong operational disruption.

KNOW THE DIFFERENCE

EDR Is the Tool. Someone Still Has to Watch It.

EDR is the tool. MDR is managing the tool. Managing the tool means a security operations center with people in it. An alert nobody acts on is not security.

“Just because you buy a golden wrench doesn't make you a mechanic.”

How Can ITS Managed EDR Help Protect Your Business?

ITS Managed EDR provides continuous endpoint oversight and expert response support to help detect, investigate, and contain threats across your devices.

Limit Threat Movement

Isolate affected endpoints when configured response criteria are met, helping reduce the risk of an incident reaching other systems.

Detect Suspicious Endpoint Activity

Identify behaviors, fileless techniques, and other activity that signature-based antivirus may not recognize.

Guide Endpoint Remediation

Access documented investigation findings and recommended steps for addressing affected devices, accounts, and systems.

Reduce the Endpoint Security Workload

Hand off agent deployment, alert investigation, policy tuning, and reporting to ITS so your team can focus on higher-priority work.

What Does ITS Managed EDR Include?

ITS Managed EDR combines endpoint technology, expert oversight, and response support for threat detection, investigation, containment, rollback, and remediation planning across covered devices. Included capabilities vary by service package, endpoint platform, and supported configuration.

Endpoint Agent Deployment and Tuning

ITS deploys and configures EDR agents across covered devices and tunes policies to fit your environment and reduce unnecessary alerts.

Continuous Threat Detection

ITS monitors endpoint activity for suspicious behavior, fileless attacks, and other threats that signature-based antivirus may not recognize.

Automated Isolation and Containment

ITS can automatically isolate affected endpoints when activity meets configured response criteria, helping limit lateral movement during investigation.

Threat Investigation and Analysis

ITS analysts review the alert, assess its severity and apparent scope, identify affected endpoints, and document recommended actions.

Remediation Guidance and Recovery Support

ITS delivers documented investigation findings, rollback guidance where supported, and recommended actions for addressing affected devices, accounts, and systems.

Detection Metrics and Reporting

ITS provides reporting on detected threats, incident activity, response actions, and policy tuning to support security planning and compliance documentation.

How Does ITS Managed EDR Work?

ITS Managed EDR operates through three stages: endpoint deployment and configuration, threat detection and response, and ongoing policy improvement.

  1. 01Deploy and Configure EDR

    ITS deploys EDR agents across covered endpoints and configures detection and response policies based on your environment and service package.

  2. 02Detect, Contain, and Investigate Threats

    When activity meets configured detection and response criteria, the platform can isolate the affected endpoint while ITS analysts investigate the alert, assess its severity, and document recommended actions.

  3. 03Measure and Improve Protection

    ITS reports on detections, investigations, and containment actions, then adjusts policies to improve alert quality and reduce unnecessary notifications.

How Much Does ITS Managed EDR Cost?

Managed EDR is included in the Secure package. The Core package includes endpoint protection rather than managed detection and response. ITS Cybersecurity and Managed IT services generally start at $125 per user per month, with coverage expanding based on your selected package.

Your final price will depend on your number of users and devices, infrastructure, compliance requirements, supported tools, and service package. Schedule a meeting below to get a personalized cost estimate for your environment.

  • Core

    The Core package includes endpoint detection, managed response, and threat isolation and containment.

  • Secure

    The Secure package adds broader capabilities such as network monitoring, threat intelligence, dark web monitoring, and vulnerability management based on your selected configuration.

ITS Service Commitments

ITS stands behind its Managed EDR services with confirmed performance commitments.

Deployment Commitment

Endpoint deployment and policy tuning in 30 days, with measurable detection metrics by day 60.

24-Hour Breach Response

If ITS misses the containment window, your first month is free.

See What Clients Say About ITS Cybersecurity Services

Hear from organizations that partner with ITS to protect their operations and build a stronger security posture.

I think... to not adopt some form of advanced security these days would be incredibly foolish. The biggest benefit ITS provides is the weight off my shoulders knowing that they're involved, and we've prepared ourselves as best as we could for any cyberthreats. That component is the most important to us.

JP HalversonVice President, McQuarrie Associates

We had an issue with a ransomware problem, and our previous IT partner could not resolve it. It brought us to a standstill... so we reached out to ITS and they helped us with the issue.

Mark BreauningerDirector of Operations, The Synthetic Grass Store

ITS identified an MFA hole in a large-scale EHR system that had never been caught before. Had it not been for them, we would've gone live and unknowingly increased our risk. Their insight not only protected us, [but it also] helped four other facilities that implemented the same system after us.

Doug McCoyCEO, Eastern Plumas Health Care (EPHC)

How Has ITS Helped Businesses Strengthen Cybersecurity?

Read stories from real clients who faced cybersecurity challenges and partnered with ITS to protect their operations.
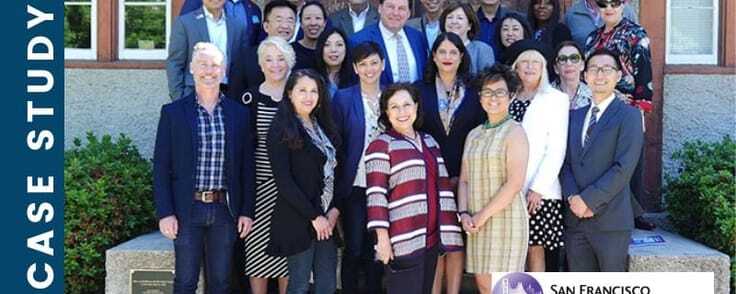
The San Francisco Association of Realtors team

How a Realtor Association Strengthened Security by Modernizing Its IT Infrastructure

Learn how ITS helped the San Francisco Association of Realtors upgrade its firewall and wireless network, modernize aging infrastructure, and achieve its security goals.
Read the Case Study →
John R. Waters & Company office

How John R. Waters & Company Found Greater Peace of Mind After Switching MSPs

Learn how John R. Waters & Company switched MSPs and gained proactive support from ITS, helping the business resolve serious cybersecurity incidents without irreversible damage.
Read the Case Study →
Adventure Photo Tours, Las Vegas

How a Tour Company Strengthened Cybersecurity Without Hiring In-House IT

Learn how Adventure Photo Tours stopped a server hack, gained 24/7 IT monitoring, and received ongoing support at a fraction of the cost of hiring full-time IT staff.

Read the Case Study →

Learn More About Endpoint Detection and Response

These resources cover key questions business leaders ask when evaluating endpoint security solutions. Learn what EDR does, how it compares with antivirus and MDR, and where it may fit within your organization's security strategy.

Computer Security and EDR

What is EDR, and Why Does My Business Need One?

Read the Article →
Anti-virus keyword on a search engine search

Antivirus vs. EDR vs. MDR: What are the Differences?

Read the Article →

Managed EDR Services: Frequently Asked Questions

What is Endpoint Detection and Response (EDR), and what does a Managed EDR service include?

Endpoint Detection and Response (EDR) is a managed service that deploys and tunes endpoint security agents to detect suspicious activity, support isolation, and assist with remediation. ITS delivers it as part of its managed cybersecurity services.

What is the difference between EDR and antivirus?

Antivirus primarily identifies known malicious files using signatures and related detection methods. EDR monitors endpoint activity for suspicious behavior and provides investigation and response capabilities. Many businesses use both as part of one endpoint security approach.

What happens when ITS EDR detects a threat?

When activity meets configured detection and response criteria, the endpoint platform can initiate containment, such as isolating the affected device. ITS analysts then investigate the incident, document their findings, and recommend remediation steps.

How long does EDR deployment take?

ITS targets endpoint-agent deployment and policy tuning within 30 days, with measurable detection metrics typically available by day 60.

Can ITS Managed EDR work with our existing endpoint environment?

Yes. ITS Managed EDR supports approved endpoint platforms, operating systems, and security configurations. During onboarding, ITS reviews your devices, current tools, technical requirements, and any coverage limitations.

Is Managed EDR included in every ITS service package?

Managed EDR is available through the Secure package. Core includes endpoint protection; Secure adds managed endpoint detection and response. Your ITS account team can help determine which package fits your environment.

Who is ITS Managed EDR designed for?

ITS Managed EDR is designed for growing and regulated organizations that need continuous endpoint monitoring and faster threat response. It is particularly valuable for businesses handling sensitive data, meeting cyber insurance obligations, or operating in regulated industries with security and compliance requirements.

Which Managed EDR Solution Is Right for Your Business?

Meet with an ITS cybersecurity expert to review your current endpoint protection, uncover security gaps, and determine the right level of Managed EDR coverage for your organization.

Get clear, practical recommendations for strengthening endpoint security across your users, devices, and IT environment.