ITS Security Division

Vulnerability Management That Closes Findings, Not Just Reports Them

Find the weaknesses that matter, prioritize them by real business risk, coordinate remediation, and verify that the problem is actually fixed.

Cybersecurity Expertise Backed by Industry Recognition

ITS has earned industry recognition for cybersecurity expertise, managed services, and technology partner performance.
  • CRN MSP 500 2026
  • CRN Tech Elite 250 2026
  • CRN Security 100 2026
  • Cloudtango's MSP Select 2026
  • SonicWall MSP Partner of the Year 2026

A Scan Finds Problems. It Doesn't Close Them.

Most organizations do not lack findings. They lack a way to decide which findings matter and a process that confirms anything actually got fixed. The CIS Critical Security Controls treat continuous vulnerability management as its own control for that reason.

Scan Results Outgrow the Team

A single scan across servers, workstations, and network devices can return more findings than any team can work through, so triage stalls before remediation starts.

Severity Is Not Priority

A high technical severity on a system nobody can reach may matter less than a moderate one on an internet-facing server, and a severity score alone cannot make that call.

Third-Party Software Gets Missed

Operating system updates are usually handled. Browsers, plugins, runtimes, and line-of-business applications are where unpatched versions quietly accumulate.

Closure Isn't Always Verified

Without a rescan, a remediation ticket marked complete and a vulnerability actually closed are two different things.

What Does Managed Vulnerability Management Do for Your Business?

ITS manages the full cycle so your team knows what is exposed, what matters most, what needs to change, and whether remediation actually worked.

Know What You Actually Have

Discovery keeps an inventory of the systems and software in scope, because anything unknown is never assessed.

Prioritize by Real Risk

Findings are ranked using exposure, how important the affected system is to your business, and whether the weakness is known to be exploited, not by score alone.

Close Findings and Prove It

Remediation is tracked through to completion and confirmed by rescanning, so closure is verified rather than assumed.

Show Progress Over Time

Reporting shows leadership how exposure is trending and where remediation is blocked, which supports both planning and audit questions.

What Does ITS Vulnerability Management Include?

Exact coverage depends on your ITS cybersecurity package, environment, and supported systems.

Asset Discovery and Inventory

Ongoing identification of the systems, devices, and software in scope, so the inventory used for scanning stays current rather than dating from onboarding.

Recurring Scanning

Scheduled internal and external scanning of supported systems, using credentialed scanning where appropriate for accurate results rather than surface-level guesses.

Risk-Based Prioritization

Prioritize findings using severity, business exposure, and evidence that a vulnerability is being actively exploited, including CISA's Known Exploited Vulnerabilities catalog.

Remediation, Not Just Detection

ITS coordinates supported patches, configuration changes, and mitigations so findings move toward closure rather than staying in a report.

Verify the Fix

Rescanning after remediation to confirm findings are closed, with anything still present returned to the queue rather than marked done.

Reporting and Exception Tracking

Document approved risk exceptions, including the rationale and any compensating controls for technical teams and leadership.

How Does ITS Vulnerability Management Work?

A repeating cycle rather than a one-off project, because new weaknesses appear in systems that were clean last month.

  1. 01Discover and Assess

    ITS establishes what is in scope, deploys or configures supported scanning, and produces a baseline of current findings.

  2. 02Prioritize and Remediate

    Findings are triaged into a working order, remediation is coordinated with your team and your change windows, and mitigations are applied where patching is not possible.

  3. 03Verify and Report

    Rescanning confirms closure, exceptions are recorded with their reasons, and reporting shows what changed since the previous cycle.

How Much Does Vulnerability Management Cost?

Vulnerability management is delivered as part of ITS cybersecurity and managed IT coverage rather than as a standalone product. Cybersecurity and managed IT services typically start at $125 per user per month.

Your final cost depends on these factors together. Schedule a meeting below to get a personalized cost estimate for your environment.

What shapes your final cost

  • Number of Users

    Coverage is priced per user, so headcount is the single largest factor.

  • Systems and Applications in Scope

    How many servers, workstations, network devices, and external systems are scanned.

  • Scanning Depth

    Whether scanning is credentialed, whether external and internal scanning are both in scope, and how much of the remediation work ITS coordinates.

  • Selected Package

    Which ITS package you choose, since coverage differs between packages.

How ITS Works With Your Team

Four working habits that separate a managed cycle from a scan report.

Triage Before Escalation

ITS reviews raw findings first so your team gets a prioritized working queue instead of scanner output.

Remediation Coordination

ITS manages supported fixes directly or coordinates with your team, change windows, and vendors where needed.

Exception Tracking

Items that cannot be fixed immediately remain visible with documented reasons and compensating controls.

Closure Verification

ITS rescans after remediation to confirm the issue is actually gone.

See What Clients Say About ITS Cybersecurity Services

Hear from organizations that partner with ITS to protect their operations and build a stronger security posture.

I think... to not adopt some form of advanced security these days would be incredibly foolish. The biggest benefit ITS provides is the weight off my shoulders knowing that they're involved, and we've prepared ourselves as best as we could for any cyberthreats. That component is the most important to us.

JP HalversonVice President, McQuarrie Associates

We had an issue with a ransomware problem, and our previous IT partner could not resolve it. It brought us to a standstill... so we reached out to ITS and they helped us with the issue.

Mark BreauningerDirector of Operations, The Synthetic Grass Store

ITS identified an MFA hole in a large-scale EHR system that had never been caught before. Had it not been for them, we would've gone live and unknowingly increased our risk. Their insight not only protected us, [but it also] helped four other facilities that implemented the same system after us.

Doug McCoyCEO, Eastern Plumas Health Care (EPHC)

How Has ITS Helped Businesses Strengthen Cybersecurity?

Read stories from real clients who faced serious cybersecurity challenges and partnered with ITS to protect their operations.
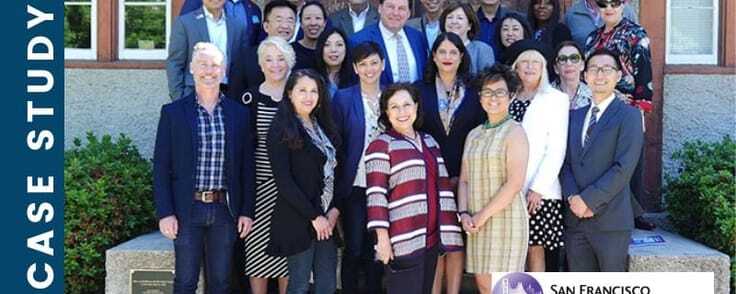
The San Francisco Association of Realtors team

How a Realtor Association Strengthened Security by Modernizing Its IT Infrastructure

Learn how ITS helped the San Francisco Association of Realtors upgrade its firewall and wireless network, modernize aging infrastructure, and achieve its security goals.
Read the Case Study →
John R. Waters & Company office

How John R. Waters & Company Found Greater Peace of Mind After Switching MSPs

Learn how John R. Waters & Company switched MSPs and gained proactive support from ITS, helping the business resolve serious cybersecurity incidents without irreversible damage.
Read the Case Study →
Adventure Photo Tours, Las Vegas

How a Tour Company Strengthened Cybersecurity Without Hiring In-House IT

Learn how Adventure Photo Tours stopped a server hack, gained 24/7 IT monitoring, and received ongoing support at a fraction of the cost of hiring full-time IT staff.

Read the Case Study →

Learn More About Vulnerability Management

These resources cover what a security vulnerability is, why scanning on a schedule matters, and what a managed vulnerability program delivers.

a person pressing on a holographic check mark indicating good vulnerability management

6 Crucial Benefits of Vulnerability Management for Businesses

Read the Article →
an alarm clock signifying a scheduled vulnerability scan

How Important is a Regularly Scheduled Vulnerability Scan?

Read the Article →
a security vulnerability in your system

What is a Security Vulnerability? (Definition, Types, and Remediation)

Read the Article →

Vulnerability Management: Frequently Asked Questions

What is vulnerability management?

Vulnerability management is the continuing process of discovering assets, identifying weaknesses in them, prioritizing those weaknesses by risk, remediating them, and verifying the fix. The CIS Critical Security Controls describe it as continuous vulnerability management, distinct from a one-time assessment.

What is the difference between a vulnerability scan and vulnerability management?

A scan is a point-in-time activity that produces findings. Vulnerability management is the process around it: inventory, prioritization, remediation, verification, and reporting. A scan without that process produces a report nobody closes.

How are findings prioritized?

Technical severity is the starting point, and the Common Vulnerability Scoring System describes that severity but not your business context. ITS also weighs whether the affected system is internet facing, how important it is to the business, whether compensating controls exist, and whether the weakness appears in the Known Exploited Vulnerabilities catalog published by CISA.

How often should scanning run?

Scanning runs on a recurring schedule and after significant change. The appropriate frequency depends on your environment, your exposure, and any compliance obligations you carry: internet-facing systems generally warrant more frequent scanning than internal ones. ITS sets the schedule with you during onboarding rather than applying one interval to everything.

Who fixes the vulnerabilities ITS finds?

ITS can remediate supported systems directly, coordinate changes with your internal IT team, or work with the relevant vendor when the fix falls outside ITS's control. Exact responsibilities depend on your service package, environment, and change-management requirements.

What happens when a vulnerability cannot be patched?

Some findings have no available fix, and some patches would break an application the business depends on. In those cases ITS documents the exception, applies mitigations such as restricting access, segmenting the system, or disabling the affected feature, and keeps the item visible instead of closing it quietly.

Does vulnerability management replace penetration testing?

No. Vulnerability management keeps known weaknesses closed across your environment over time. A penetration test establishes what an attacker could chain together at a point in time. NIST treats them as different activities in its guidance on security testing and assessment, and organizations that take security seriously generally do both.

Do You Know Which Weaknesses Are Still Open?

Meet with an ITS cybersecurity expert to review your current scanning coverage, how findings get prioritized, and what it would take to close them and keep them closed.